Hello,
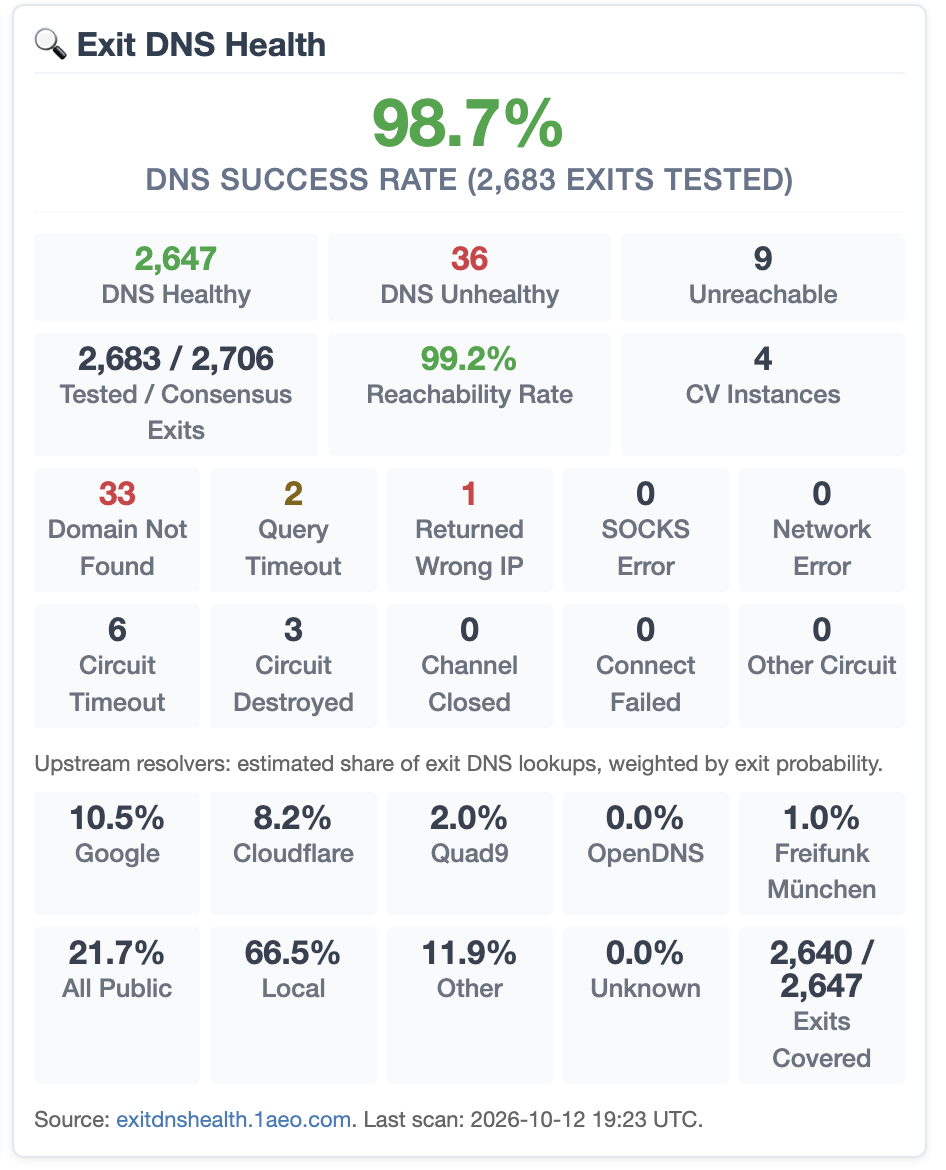
Exit DNS health checks now include the recursive resolver each exit used. Results are on https://exitdnshealth.1aeo.com (raw) and https://metrics.1aeo.com (aggregated and specific)
Methodology
Each exit is probed with unique values with tor.exit.validator.1aeo.com to bypass caching and capture the authoritative query's source IP. Upstream resolvers are classified once a threshold of ~25 queries per relay is met:
Local: Query originates from the exit's IP or its origin AS (including hoster-internal resolvers).
Public: Google Public DNS, Cloudflare, Quad9, OpenDNS, or Freifunk München.
Other: Uncategorized third-party resolvers.
Current Network Snapshot (12 Oct 2026)
Across ~2,600 exits with sufficient query volume:
Local: ~67%
Public: ~22% (~510 exits: Google ~10%, Cloudflare ~8%, Quad9 ~2%, Freifunk ~1%, OpenDNS <1%)
Other: ~12%
Endpoints
Per-relay status: [https://metrics.1aeo.com/relay/](https://metrics.1aeo.com/relay/)<FINGERPRINT>/ (DNS Health → Upstream Resolver)
Aggregated dashboard: [https://metrics.1aeo.com/network-health.html](https://metrics.1aeo.com/network-health.html)
Raw JSON: [https://exitdnshealth.1aeo.com/latest.json](https://exitdnshealth.1aeo.com/latest.json) (metadata.resolvers, results[].resolver)
Prometheus scrape: [https://metrics.1aeo.com/metrics](https://metrics.1aeo.com/metrics) (aeo1_exit_dns_public_resolver_share_ratio, aeo1_exit_dns_resolver_queries_count)
As a reminder, community best practices recommend running a local non-forwarding recursive resolver (e.g., Unbound or BIND on 127.0.0.1) rather than pointing to centralized public DNS providers to prevent upstream query correlation and metadata logging.